
-
Product Categories
-
Live Support Chat

Crack MCU ATmega16 Binary: Technical Analysis of Firmware and Memory Protection
1. ATmega16 Architecture and Binary Structure
Crack MCU ATmega16 Binary is a technical search term associated with examining, analyzing, and recovering program information from the ATmega16 microcontroller. Originally developed by Atmel, now part of Microchip Technology, the ATmega16 is an 8-bit AVR microcontroller featuring 16 KB of in-system programmable Flash, 1 KB of SRAM, and 512 bytes of EEPROM. Its integrated peripherals include timers, PWM channels, an ADC, serial communication interfaces, and a JTAG debugging interface. These capabilities have made the device useful in industrial control equipment, instrumentation, embedded automation, consumer electronics, and legacy electronic products. The binary stored in its Flash memory contains compiled machine instructions rather than the original human-readable source code. Understanding this distinction is essential when evaluating firmware preservation, reverse engineering, and embedded software restoration.
2. Why ATmega16 Binary Analysis Can Be Challenging
The original source code, development project, software archive, and programming documentation for an established electronic product may become unavailable over time. In such circumstances, the programmed microcontroller can provide important evidence about the original system’s operation. The objective of Crack MCU ATmega16 Binary analysis is to determine whether firmware, memory contents, configuration information, or other relevant data can be accessed and examined.
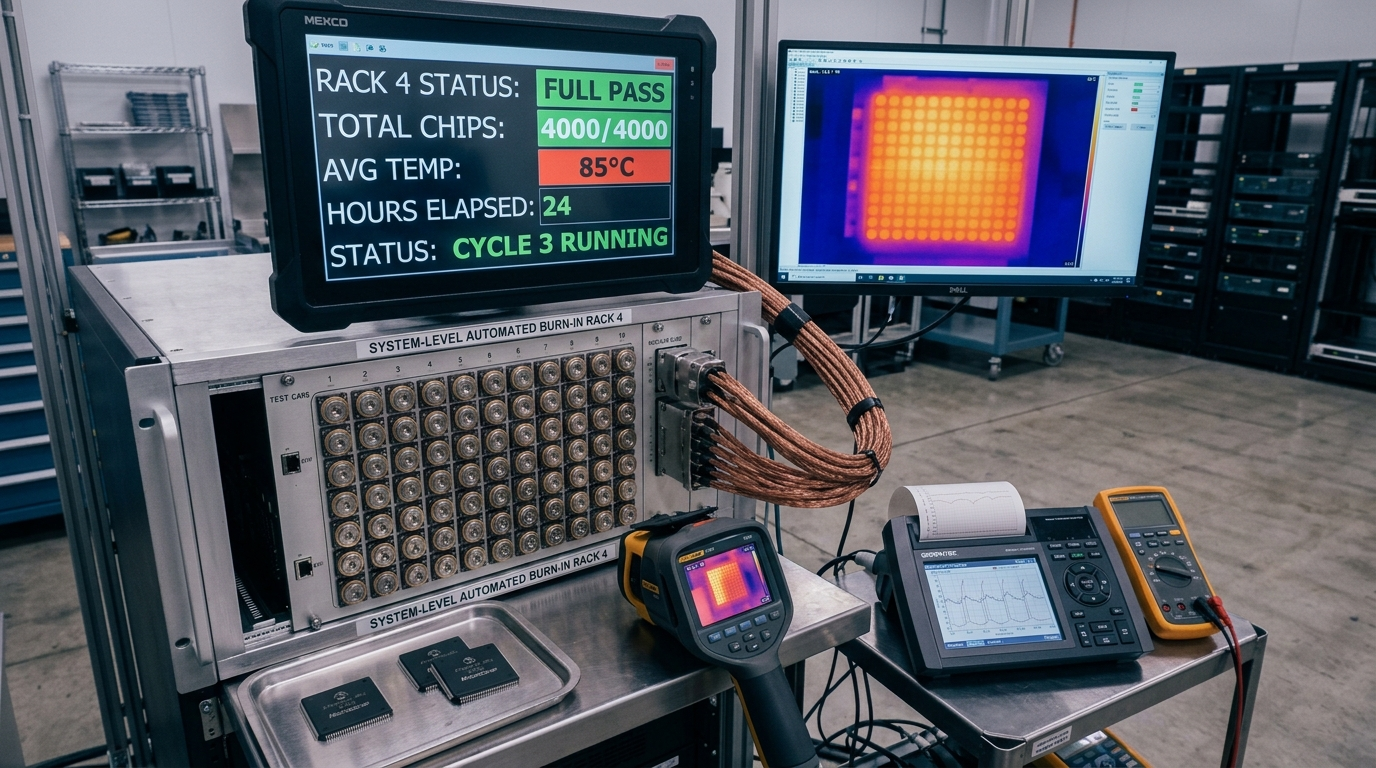
The ATmega16 implements programmable memory lock bits that restrict certain external programming and verification operations. Depending on their configuration, these protective settings can prevent standard tools from reading or verifying Flash and EEPROM contents. Microchip’s ATmega16 documentation explains that the documented chip-erase operation clears the lock bits, but it also erases the program and data memory. Consequently, chip erase is not a method for preserving firmware from a locked device. Engineers must evaluate the protection status before performing any operation that could destroy valuable memory contents. Microchip ATmega16 datasheet.
3. Technical Methods for Crack MCU ATmega16 Binary Analysis
A structured Crack MCU ATmega16 Binary investigation begins with confirming the chip identity, inspecting the PCB, documenting the power supply and clock configuration, and identifying available programming or debugging interfaces. Engineers can then assess the Flash memory, EEPROM, SRAM, fuse settings, and lock-bit configuration to establish which information may be accessible.
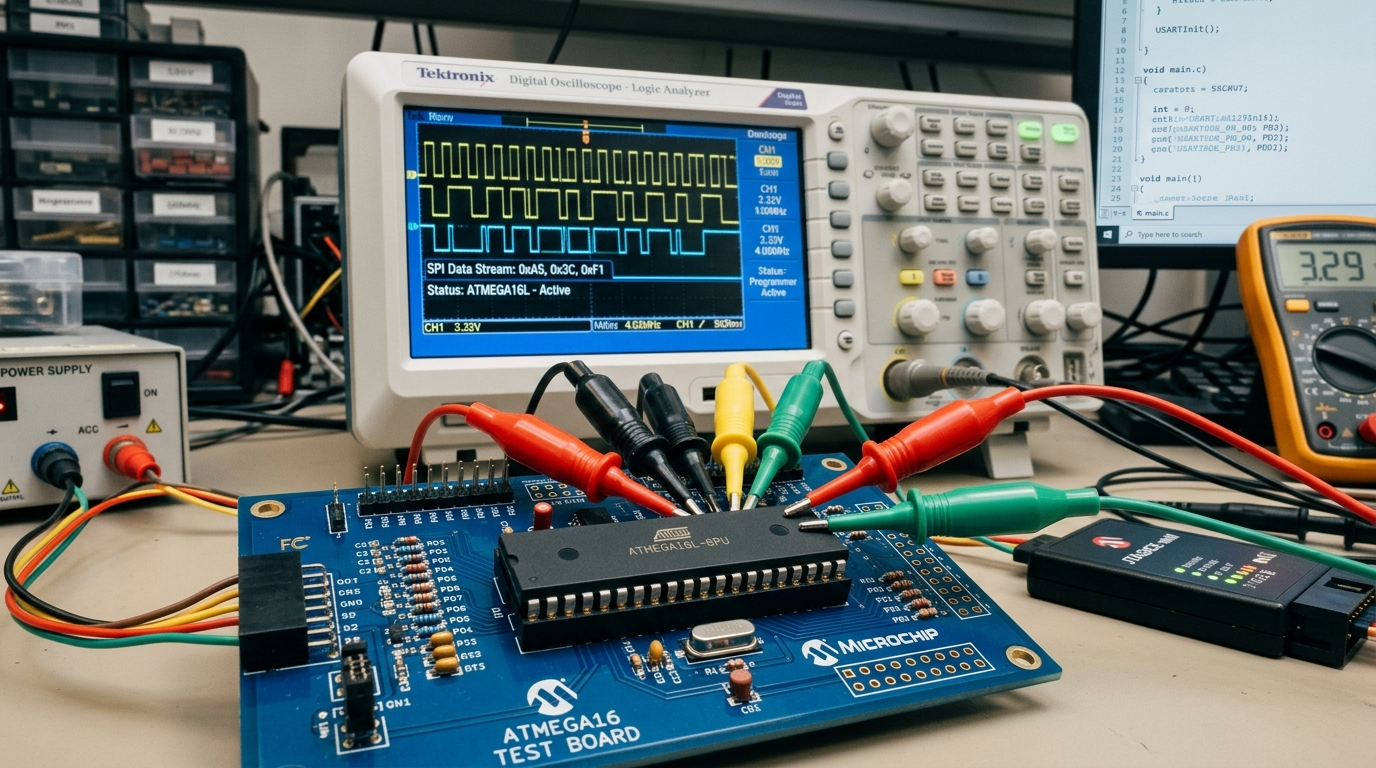
When a legitimate binary image is available, static analysis can help identify instruction sequences, interrupt vectors, constants, lookup tables, peripheral initialization routines, and communication logic. AVR disassembly tools can translate machine instructions into assembly language, while firmware comparison tools can identify differences between binary versions. These techniques support software behavior analysis even when the original source code is missing.
The terms readout, copy, and unlock describe different technical objectives and should not be treated as interchangeable operations. Readout means obtaining accessible memory contents; copying preserves an available binary image; unlocking concerns changing or removing an access restriction. A locked, secured, or protective configuration can prevent standard readout, and the documented chip-erase procedure destroys the existing memory contents. Additional techniques should therefore be considered only after the device architecture and applicable limitations have been assessed.
4. Firmware Preservation and Reverse Engineering
The technical value of Crack MCU ATmega16 Binary analysis extends beyond extracting a file. A preserved firmware image can support binary comparison, fault investigation, hardware replacement, legacy-product maintenance, and documentation of embedded behavior. EEPROM data may also contain calibration values, operating parameters, or application-specific settings that are distinct from the executable Flash program.
It is important to recognize that a recovered binary is not equivalent to the original source code. Reconstructing readable source code from machine instructions is a separate reverse-engineering task, and the result may not reproduce the original variable names, comments, project structure, or build environment. Similarly, the presence of encrypted data should not be assumed merely because a device is locked; memory access protection and cryptographic encryption are different mechanisms.
A reliable approach to Crack MCU ATmega16 Binary therefore combines device identification, non-destructive inspection, memory-protection assessment, binary analysis, and careful documentation. The achievable outcome depends on the actual chip condition, protection configuration, and availability of a valid firmware image. Understanding these factors helps preserve embedded software knowledge while avoiding unnecessary data loss during technical investigation.